Cybersecurity giant Symantec plays down unreported breach of test data

The American cybersecurity giant Symantec has downplayed a data breach that allowed a hacker to access passwords and a purported list of its clients, including large Australian companies and government agencies.

The list extracted in the February incident, seen by Guardian Australia, suggests that all major federal government departments were among the targets of a hacker who also claimed to be responsible for Medicare data being available for sale on the dark web.

But Symantec said the “minor incident” involved “an isolated, self-enclosed demo lab in Australia – not connected to Symantec’s corporate network – used to [demonstrate] various Symantec security solutions and how they work together”.

The incident was not reported because Symantec concluded that “no sensitive personal data was hosted in or extracted from this demo lab, nor were Symantec’s corporate network, email accounts, products or solutions compromised”.
The US cybersecurity company Symantec says a data breach that allowed a hacker to access passwords and a purported list of its clients was a ‘minor incident’. Photograph: SOPA Images/LightRocket via Getty Images

The hacker extracted a list of purported clients of Symantec’s CloudSOC services, account managers and account numbers – but Symantec insists data contained in the system were “dummy e-mails and a small number of low-level and non-sensitive files for demonstration purposes” in a demo lab “not used for production purposes”.

The list of purported clients includes the Australian federal police, the big four banks, insurers, universities, retailers and departments in the New South Wales and federal public service.

“This is an old list of some of the largest public and private entities in Australia – it was in the environment for testing purposes,” a Symantec spokeswoman said. “These entities are not necessarily Symantec customers, nor do we necessarily host services for them.”

Several federal departments, including infrastructure, industry, human services and finance, confirmed that they do not use Symantec’s CloudSOC services and do not store information with Symantec. But Guardian Australia understands that others queried the “minor” breach with Symantec because they are customers.

The Department of Social Services said it “uses Symantec products including CloudSOC, in line with Australian Cyber Security Centre best practice”.

“The product in question is not used by the department to store customer, or sensitive information.”

In a statement the Department of Infrastructure, Transport, Cities and Regional Development noted the department name referenced in the list was “discontinued in 2013”.

“We have received no notice from Symantec regarding this matter, but we will make contact in relation to their continued use, if any, of our department name.”

In a statement the Department of Home Affairs said it “does not use the Symantec CloudSOC services, however does use a number of other Symantec products on the department’s internal network, that are managed by departmental staff”.

“The department does not have any sensitive information that is held by Symantec.

“Information held by Symantec would relate to Symantec’s commercial relationship with the department, which is publicly available information.”

The departments of agriculture, education, employment, communication and arts said they used other Symantec products, but not cloud services, and did not store information with Symantec. Education also said it would “make contact in relation to their use of our department name”.

The Australian Privacy Act creates a scheme for compulsory notification when a data breach is likely to result in serious harm to individuals whose personal information is involved in the breach.

The Symantec spokeswoman said it treated “any cyber-security incident – regardless of its scope or severity – with the utmost priority and take great caution in complying with the laws of the countries in which we do business around the world”.

“Consistent with our internal policies and guidance, which align with national and international data protection laws, no sensitive personal data or information has been disclosed that would trigger any regulatory obligations, but Symantec will continue to take appropriate remediation efforts if the situation changes.”
The Guardian

Other News

Hanoi approves controlled pilot of two technology projects

Hanoi approves controlled pilot of two technology projects

The two projects involve an intelligent autonomous transportation system developed by Phenikaa-X JSC and a technology for producing mixed rare-earth oxides with a purity of over 95% on a semi-industrial scale developed by the Mining Technology and Construction Consultancy JSC.

Banking industry in AI era: When data becomes competitive advantage

Banking industry in AI era: When data becomes competitive advantage

In just a few years, AI has evolved from an experimental technology into an “assistant” for many banks, supporting everything from customer service, credit approval, and fraud detection to risk management. However, as the technological gap between institutions narrows, a new question is emerging: What will determine banks' competitive advantage in the AI era?

Bac Ninh considers establishing AI centre of excellence

Bac Ninh considers establishing AI centre of excellence

A meeting has been held in Bac Ninh to discuss potential cooperation with Plug and Play in developing the northern province’s innovation ecosystem and establishing an artificial intelligence (AI) centre of excellence, with Standing Vice Chairman of the provincial People’s Committee Mai Son receiving a delegation from the global innovation platform.

Hanoi allows 24-month trial of autonomous vehicles at Hoa Lac

Hanoi allows 24-month trial of autonomous vehicles at Hoa Lac

The project aims to assess the safety, reliability and readiness of autonomous vehicles under real traffic conditions, as well as the effectiveness of autonomous public transport and compatibility with existing systems. Its results will contribute to developing technical standards, operating procedures and management models suited to Hanoi’s traffic conditions.

Singapore's experience suggests solutions to Vietnam's human resources challenge in AI era

Singapore's experience suggests solutions to Vietnam's human resources challenge in AI era

As Vietnam accelerates digital transformation and high-tech development, Singapore’s experience and the engagement of global technology companies demonstrate that human resources preparation must stay ahead of the curve. The ability to filter knowledge, collaborate, innovate and effectively use AI will increasingly become essential to helping workers adapt to a changing labour market and strengthening the competitiveness of Vietnam’s economy in the new era.

Protecting national security amid digital transformation, cyberspace

Protecting national security amid digital transformation, cyberspace

Cybersecurity, information security and data security risks must be identified and addressed early and from afar, with appropriate defensive measures ready to neutralise threats and protect national interests in cyberspace, said Lieutenant General Le Xuan Minh, Director of the Ministry of Public Security’s Department of Cybersecurity and Hi-tech Crime Prevention (A05).

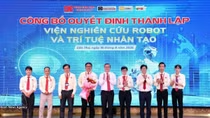
Mekong Delta launches first robotics, AI research institute

Mekong Delta launches first robotics, AI research institute

Dr. Nguyen Van Quang, Rector of Nam Can Tho University, said the university is developing a value chain covering training, research, technology development, testing, technology transfer and commercialisation. The model is designed to link research more closely with practical needs, ensuring that technologies generate products and products create value for society.

Vietnam positioned to harness AI wave, World Bank report says

Vietnam positioned to harness AI wave, World Bank report says

The WB report identifies Vietnam as one of the few economies outside the European Union (EU) to have adopted a comprehensive AI regulatory framework as early as 2025. Vietnam applies a risk-tiered approach similar to that of the EU AI Act, imposing different obligations depending on whether an AI system poses “unacceptable,” “high,” “low” or “minimal” risks. The approach is viewed as a strategic step towards ensuring safe and transparent AI governance.

AI offers both opportunities, challenges for Vietnam's growth

AI offers both opportunities, challenges for Vietnam's growth

Dr. Ho Duc Thang, a full-time member of the National Assembly’s Committee for Cultural and Educational, said productivity is the key to sustaining double-digit economic growth, and AI has greater potential to improve productivity than any previous technology.

Top leader unveils people-centred vision for new development model

Top leader unveils people-centred vision for new development model

Vietnam's growth model, long fueled by low-cost labour, resource extraction, contract manufacturing, expanded investment, and capital accumulation, has run out of road. The country now needs a sweeping reform agenda to shift from extensive growth to a model driven by productivity, knowledge, science and technology, innovation, and digital transformation.